Syrian Hacker Gets Prison Time in US After Over a Decade on the Run
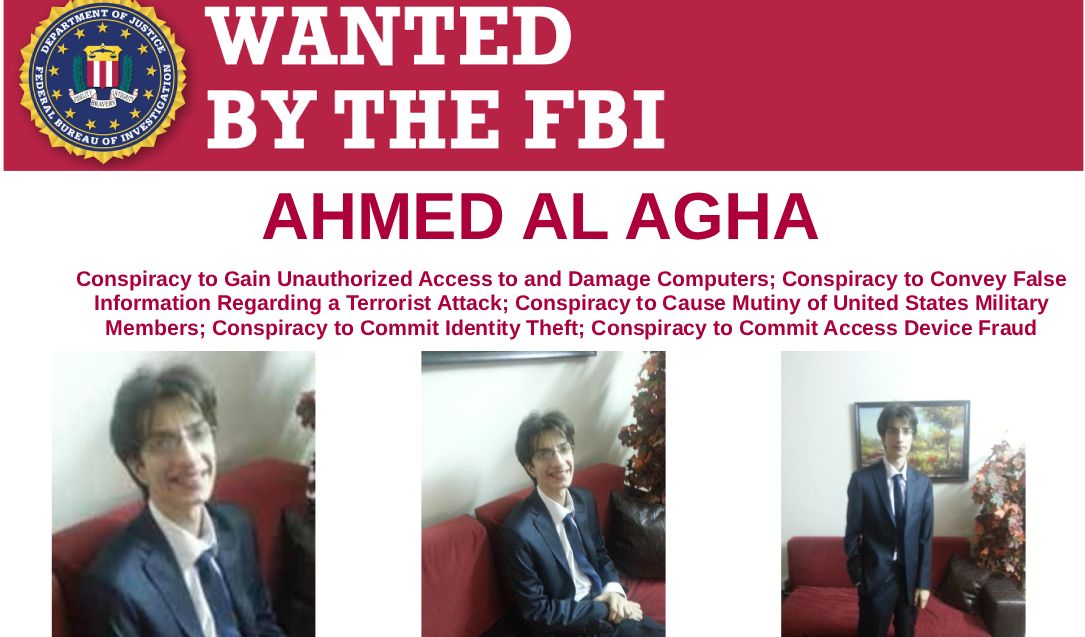
A US court sentenced Syrian hacker Ahmad Umar Agha to 42 months for pro-Assad attacks on media, businesses, and government entities. The post Syrian Hacker Gets Prison Time in US After Over a Decade on the Run appeared first on SecurityWeek.
Attackers Exploit Critical Drupal Commerce Core Vulnerability CVE-2026-118539
Drupal warns that attackers are exploiting a critical authorization flaw in Commerce Core, putting vulnerable online stores at risk. Drupal warns that threat actors are exploiting a highly critical security flaw, tracked as CVE-2026-118539, in its Commerce Core module. The vulnerability is caused by missing authorization checks. “This module enables you to sell goods and […]
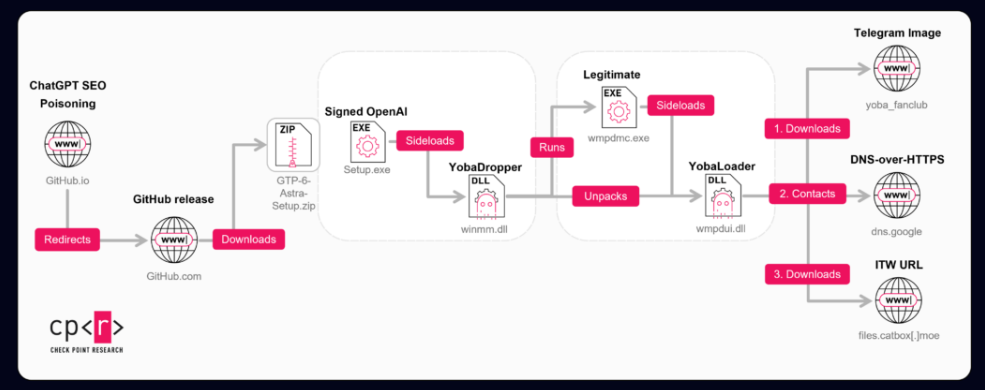
Yoba Malware Hides a Crypto Miner Behind Legitimate OpenAI and Anthropic Binaries
Yoba malware uses fake ChatGPT and Claude apps to sideload malware through signed installers and deploy a cryptocurrency miner. Check Point Research has spent two months tracking a campaign it calls Yoba, which uses the popularity of AI tools to spread a custom malware chain. The attackers build fake GitHub projects that pose as AI […]
The Record Breach
DOJ raises privacy concerns over potential sale of Character.AI chats
The DOJ’s Executive Office for U.S. Trustees said a consumer privacy ombudsman is needed to advise the court on how to regulate what data from Character.AI can be sold and under what terms.
 Security Affairs Vuln
U.S. CISA adds GitLab and Cisco flaws to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds GitLab and Cisco flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added GitLab and Cisco vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: Below are the flaws added to the catalog: CVE-2026-97229 is a critical security flaw that could let attackers run code on […]
Fashion retailer Resolve says hackers stole payment card information
The company, billing itself as “the next-generation fashion retailer for Millennial and Generation Z consumers,” said a recent hack exposed customer payment card numbers.
 Security Affairs Breach
$6.3 Billion Stolen from Binance in Attack Attributed to North Korea
Binance links a $6.3 billion crypto theft to a compromised DevOps laptop, with North Korean hackers blamed by blockchain analysts. Binance was investigating suspicious transfers that early estimates put at up to $5.8 billion. A day later, multiple media outlets reported that the largest cryptocurrency exchange had linked the theft of about $6.3 billion to […]
Florida warns that 4.9 million people had Social Security numbers leaked in financial aid site breach
The state’s Department of Education (FLDOE) said on Thursday it became aware of a data breach involving the Florida Student Financial Aid website on October 19.
 SecurityWeek Vuln
PHP2Shell Attacks Root Palo Alto Firewalls but Fail Against WordPress
Over 22.6 million exposed instances are potentially affected by the critical PHP flaws that have been targeted for over a week. The post PHP2Shell Attacks Root Palo Alto Firewalls but Fail Against WordPress appeared first on SecurityWeek.
 SecurityWeek Breach
In Other News: Anthropic Breach Dispute, UEFI Flaw Hits Most Servers, Cloudflare AI Data Leak
Noteworthy stories that might have slipped under the radar: Iran eyed in military freezer hacks, Copenhagen University breach, AI-powered malware. The post In Other News: Anthropic Breach Dispute, UEFI Flaw Hits Most Servers, Cloudflare AI Data Leak appeared first on SecurityWeek.
Syrian Electronic Army hacker gets prison time for attacks on Western targets
Ahmad Umar Agha, known online as “Th3Pr0,” was sentenced Thursday in federal court in Virginia to 42 months behind bars for his role in a conspiracy that was organized by former Syrian President Bashar al-Assad's closest advisers.
 SecurityWeek Breach
Passkeys Are Better Than Passwords. But They Are Not Enough.
As organizations eliminate passwords, attackers will adapt. Instead of attacking the authenticator directly, they will look for opportunities around it. The post Passkeys Are Better Than Passwords. But They Are Not Enough. appeared first on SecurityWeek.
 SecurityWeek Malware
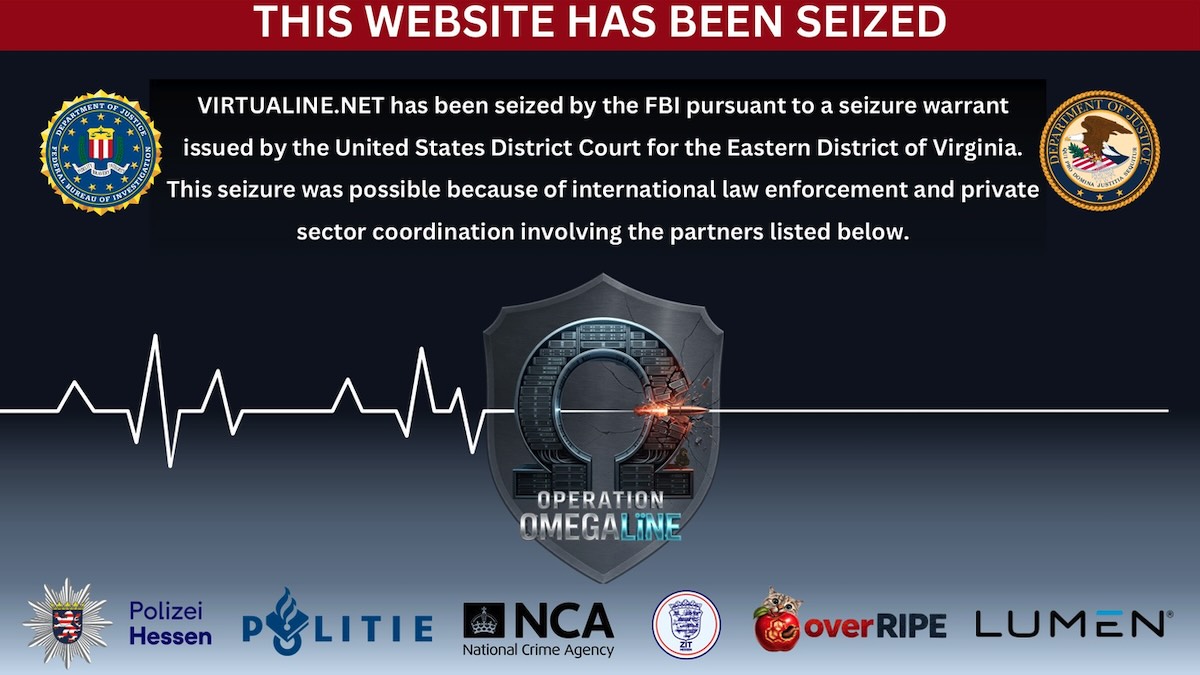
Bulletproof Host Virtualine Loses Its Domain to FBI Seizure
It allowed customers to host hack-for-hire services, supported ransomware and infostealer operators, and accepted crypto payments. The post Bulletproof Host Virtualine Loses Its Domain to FBI Seizure appeared first on SecurityWeek.
British spy agency cannot account for thousands of data storage devices, watchdog says
The Investigatory Powers Commissioner’s Office (IPCO) in its annual report for 2025, published Thursday, said it was “very concerned” and “disappointed with the time it has taken GCHQ to investigate” the issue.
Hackers target government Windows systems in Asia with new malware
The previously unknown malware, dubbed NetamLoader, uses legitimate Microsoft software components to execute malicious code, evade security tools and download additional programs onto infected computers.
 Security Affairs Breach
How to prioritize remediation after a pentest: a practitioner workflow
A practical pentest workflow combines CVSS, EPSS and business impact to validate findings, prioritize fixes and document remediation decisions. Remediation prioritization after a pentest is the process of ranking and ordering security findings based on their risk, exploitability, and business impact. A penetration test can produce any number of findings, ranging from the very low […]
 SecurityWeek Vuln
Fresh WordPress Vulnerability in Attackers’ Crosshairs
Threat actors are attempting to exploit a high-severity unauthenticated race condition leading to remote code execution. The post Fresh WordPress Vulnerability in Attackers’ Crosshairs appeared first on SecurityWeek.
Polymarket confirms cyberattack on third-party provider after outages
The company suffered outages starting at 2pm EST on Thursday and eventually attributed the downtime to a compromise involving an unnamed provider.
Russian popular home goods chain faces days of disruption following cyberattack
Poryadok, which operates 48 stores across 32 Russian cities, first reported technical problems on Sunday, saying its website, mobile app and physical stores were temporarily unavailable.
 SecurityWeek Vuln
Drupal Commerce Core Vulnerability Exploited Against Online Stores
Drupal says a highly critical Commerce Core access bypass is exploited in the wild and urges store owners to audit their orders. The post Drupal Commerce Core Vulnerability Exploited Against Online Stores appeared first on SecurityWeek.
 SecurityWeek Breach
$2 Million+ Drained From Polymarket Traders in New Supply Chain Attack
Malicious code linked to a website monitoring tool was designed to hijack logged-in Polymarket sessions and siphon user funds. The post $2 Million+ Drained From Polymarket Traders in New Supply Chain Attack appeared first on SecurityWeek.
 SecurityWeek Vuln
Max-Severity GitLab Vulnerability Exploited Against Alpine Linux
Tracked as CVE-2026-97229, the bug allows unauthenticated attackers to execute arbitrary code on the server. The post Max-Severity GitLab Vulnerability Exploited Against Alpine Linux appeared first on SecurityWeek.
 SecurityWeek Vuln
TeamViewer Flaw Could Let Malicious Hosts Take Over Support Technicians’ Machines
An integer overflow tracked as CVE-2026-111585 could be used to execute arbitrary code on the viewer’s system. The post TeamViewer Flaw Could Let Malicious Hosts Take Over Support Technicians’ Machines appeared first on SecurityWeek.
 SecurityWeek Breach
$6 Billion Binance Hack Bears Hallmarks of North Korea’s TraderTraitor
Blockchain analysts link the record crypto theft to North Korean hackers, as Binance probes a possibly compromised engineer laptop. The post $6 Billion Binance Hack Bears Hallmarks of North Korea’s TraderTraitor appeared first on SecurityWeek.
 Security Affairs Breach
Hacker leaks data on more than 40,000 Homeland Security employees
A hacker leaks personal data on more than 40,000 DHS employees, including CBP, ICE and CISA staff, after an undisclosed breach. Personal details of thousands of U.S. Department of Homeland Security (DHS) employees are now online after a hacker stole reams of data in a data breach that occurred earlier this year and nobody had […]
Binance hit by record $6.3 billion crypto hack, scrambles to freeze funds
Binance, the world's largest cryptocurrency exchange, confirmed Thursday that it had been hacked in a $6.3 billion cyber heist that blockchain investigators are blaming on North Korea.
 Security Affairs Breach
Binance Investigates Suspicious Crypto Transfers Worth Up to $5.8 Billion
Binance probes suspicious crypto transfers worth up to $5.8 billion as Tether and Circle freeze $1.79 billion in stablecoins linked to the activity. Binance is investigating a potential security incident after billions of dollars in cryptocurrency moved from wallets linked to the exchange on October 29. The transfers raised concerns about a possible hack, while […]
 Security Affairs Breach
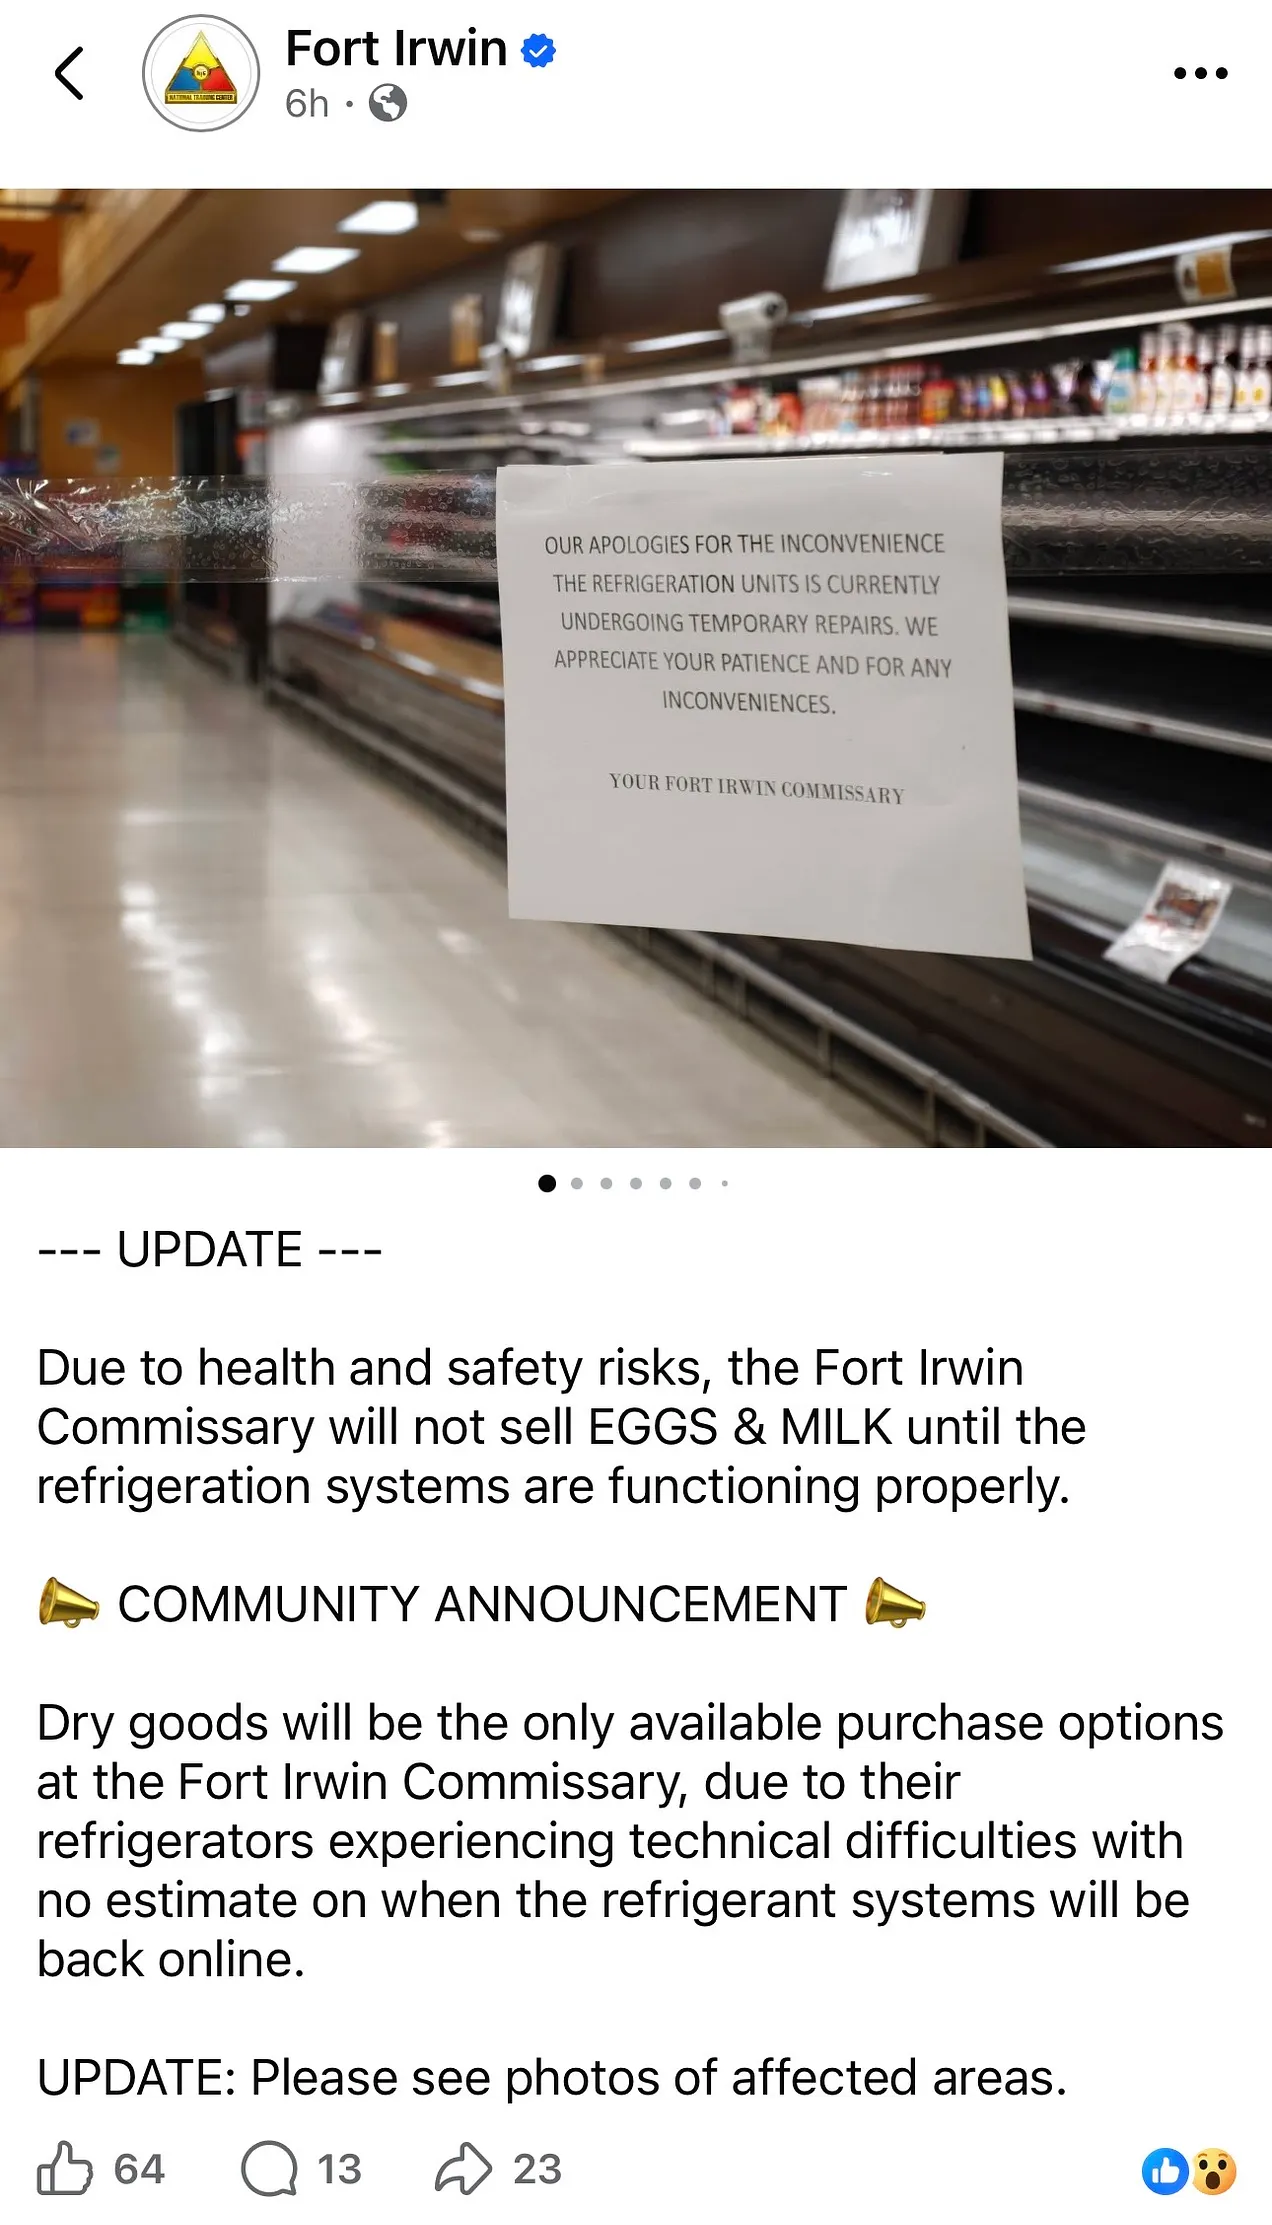
US Probes Suspected Hack Behind Military Base Freezer Failures
The Pentagon treats August freezer failures at US military bases as a suspected hack and is working with French investigators after a supermarket attack. The Pentagon is investigating freezer failures that spoiled food at US military bases in August as a suspected cyberattack, according to four officials who spoke to Reuters. One official said US […]
Limited reports of PHP bug exploitation emerge
One cyber firm listed a half-dozen exploitations of the PHP2Shell bugs, and another identified a well targeted, suspected Chinese campaign that breached U.S. "government affiliated" servers.
GM settles with 36 states for selling driver data, agrees to $220 million fine and reforms
General Motors agreed to pay $220 million to settle a lawsuit filed by a coalition of 36 state attorneys general who alleged the company unlawfully sold information about driver behavior to outside parties.
 Security Affairs Breach
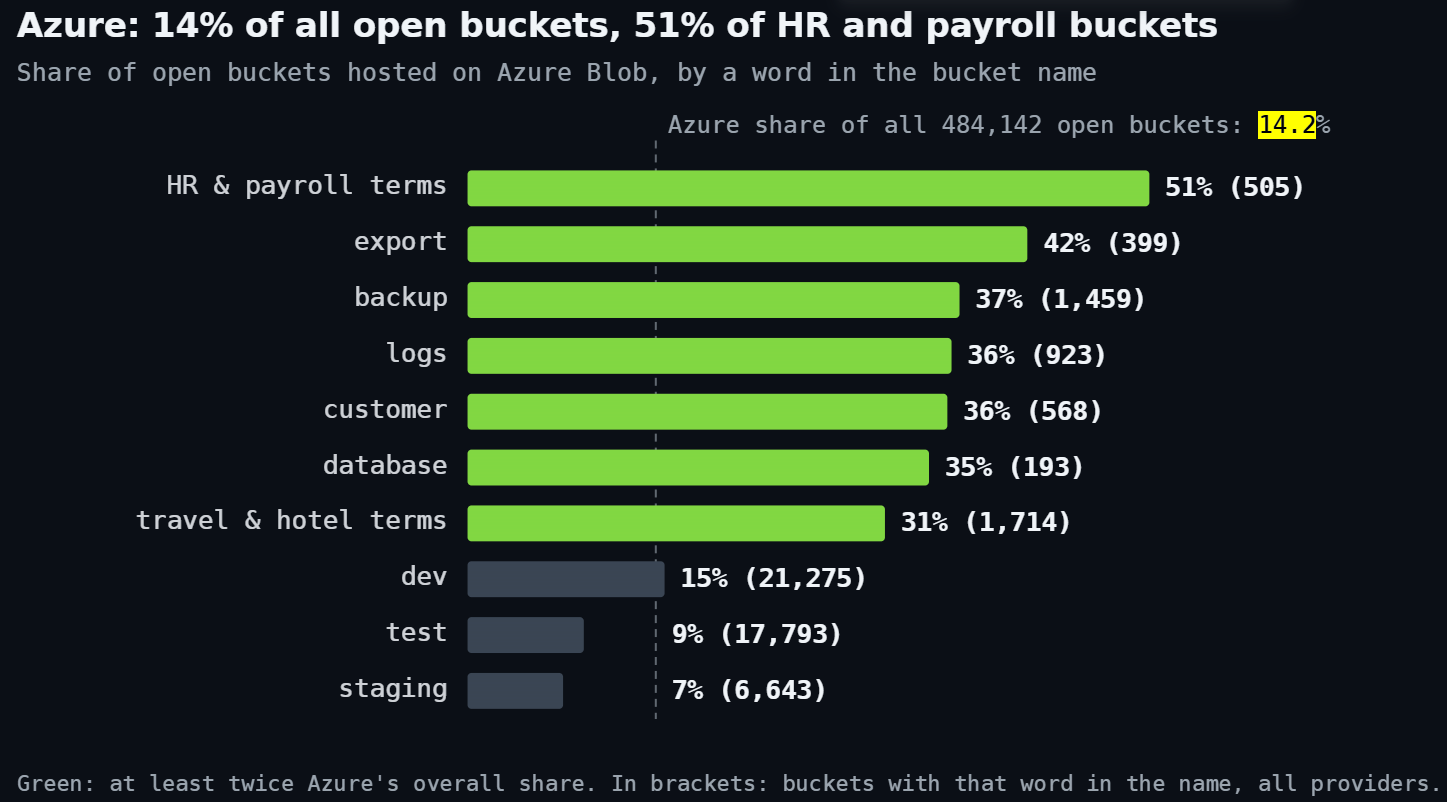
484,142 Exposed Cloud Buckets Contain 18 Billion Files
42 publicly listable cloud buckets containing 18 billion files, including exposed credentials, database dumps and backups. The Ransomnews research team counted 484,142 publicly listable cloud storage buckets in October 2026, holding 18.05 billion files. They built the count from the search engines that index open cloud storage and published it as the Ransomnews Cloud Exposure […]
 SecurityWeek Breach
When Risk Becomes Personal: What Security Leaders Can Learn From a Cancer Diagnosis
Risk managers are trained to spot weak signals, plan for disruption and make hard decisions under uncertainty. But the discipline looks different when the risk is not a system or an enterprise, but you. The post When Risk Becomes Personal: What Security Leaders Can Learn From a Cancer Diagnosis appeared first on SecurityWeek.
Federal bankruptcy courts contractor says no data stolen during cyber intrusion
"No data was extracted,” a spokesperson for BAE Systems, a federal contractor, told Recorded Future News about its probe into a cyberattack against its systems for federal bankruptcy courts.
 Security Affairs Vuln
U.S. CISA adds Linux Kernel and Broadcom VMWare ESX flaws to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Linux Kernel and Broadcom VMWare ESX flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Linux Kernel and Broadcom VMWare ESX vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: Below are the flaws added to the catalog: In July, Broadcom released patches to address […]
 SecurityWeek Vuln
Google Says Gemini 4 Carbon Leads in Finding, Exploiting and Fixing Vulnerabilities
Google’s new frontier model scored 88.2% on SEC-bench Pro and is rolling out first to vetted cyber defenders via its Fairwind Program. The post Google Says Gemini 4 Carbon Leads in Finding, Exploiting and Fixing Vulnerabilities appeared first on SecurityWeek.
 SecurityWeek Breach
How Secure Are US Elections? Voting Machine Risks and the Growing Threat of AI
Unpatched voting machines, unverifiable QR-coded ballots, and AI-driven influence campaigns leave US elections short of secure. The post How Secure Are US Elections? Voting Machine Risks and the Growing Threat of AI appeared first on SecurityWeek.
 SecurityWeek Breach
Cisco Open Sources Quarry to Catch AI Agent Attacks Hidden in Harmless Steps
Cisco open sourced Project Quarry, a rule language for detecting AI agent attacks that only emerge across sequences of benign actions. The post Cisco Open Sources Quarry to Catch AI Agent Attacks Hidden in Harmless Steps appeared first on SecurityWeek.
FTC to probe airlines, gig worker firms over personalized pricing and pay
The Federal Trade Commission ordered nine food delivery, airline and ride-sharing companies to turn over detailed information on how they harness personal data to set individual consumer prices and employee compensation.
 SecurityWeek Vuln
Adobe, Veeam, Juniper Networks Patch Critical Vulnerabilities
The flaws could lead to arbitrary code execution, authorization bypasses, and privilege escalation. The post Adobe, Veeam, Juniper Networks Patch Critical Vulnerabilities appeared first on SecurityWeek.
Cyberattack disrupts Belgian tax services before filing deadline
The Federal Public Service Finance (FPS Finance), which oversees taxation and other financial administration, said Wednesday that it was investigating the extent of the attack and had temporarily suspended access to MyMinfin, the country's main online platform for managing tax and financial affairs.
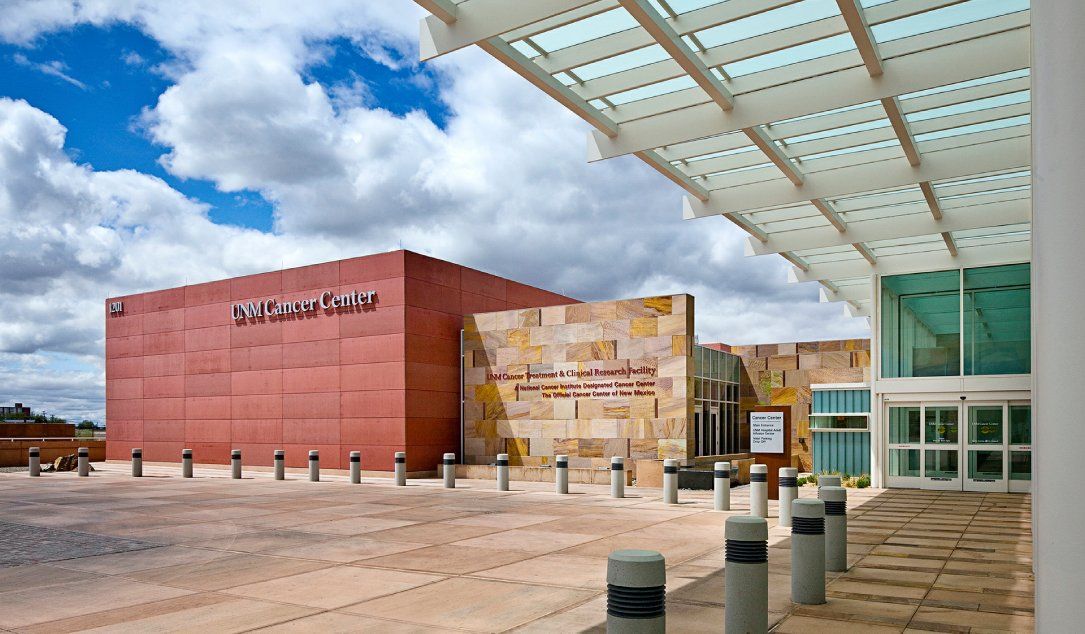
University of New Mexico restores hospital systems, urges no contact with hackers
The University of New Mexico was able to restore systems used by its healthcare facilities after a cyberattack forced it to divert ambulances and cancel classes at its medical school.
 SecurityWeek Breach
BAE Says No Data Extracted in Incident Hitting Bankruptcy Courts
BAE Systems says no data was extracted and no PII was breached in the incident that disrupted US bankruptcy court notices for weeks. The post BAE Says No Data Extracted in Incident Hitting Bankruptcy Courts appeared first on SecurityWeek.
 SecurityWeek Breach
Over 41,000 DHS Employee Records Leaked Online
The personal and work information was allegedly stolen from an Okta single sign-on system earlier this year. The post Over 41,000 DHS Employee Records Leaked Online appeared first on SecurityWeek.
 SecurityWeek Breach
Hackers Steal 2.6 Million Records From Sony’s Japanese ISP So-net
The data of So-net and Plala customers in Japan was exposed, along with 54,401 email account passwords and 16 bank account records. The post Hackers Steal 2.6 Million Records From Sony’s Japanese ISP So-net appeared first on SecurityWeek.
 Security Affairs Vuln
Volt Typhoon Used Silent Train to Hide Zero-Day Attacks
Volt Typhoon used disposable relay chains to hide zero-day attacks on critical systems. Lumen linked Silent Train to at least four zero-days. Lumen’s Black Lotus Labs has spent three years tracking a covert network it calls Silent Train, which it ties to Volt Typhoon, the China-linked APT group. The cybersecurity firm says the network hid […]
 SecurityWeek Vuln
Cisco SD-WAN Zero-Day Exploitation Tied to Volt Typhoon’s ‘Silent Train’ Network
Cisco Talos linked SD-WAN key-stealing malware to infrastructure overlapping Volt Typhoon’s Silent Train network, which Lumen detailed. The post Cisco SD-WAN Zero-Day Exploitation Tied to Volt Typhoon’s ‘Silent Train’ Network appeared first on SecurityWeek.
 SecurityWeek Vuln
Attackers Exploit Second Cisco Firewall VPN Zero-Day Since August
Cisco on Wednesday released fixes for an exploited vulnerability affecting its Secure Firewall Adaptive Security Appliance (ASA) and Secure Firewall Threat Defense (FTD) software. Tracked as CVE-2026-76418 and assigned a CVSS score of 8.6, the bug resides in the Remote Access SSL VPN service. Attackers can exploit it remotely, without authenticating, to force the device […] The post Attackers Exploit Second Cisco Firewall VPN Zero-Day Since August appeared first on SecurityWeek.
 Security Affairs Breach
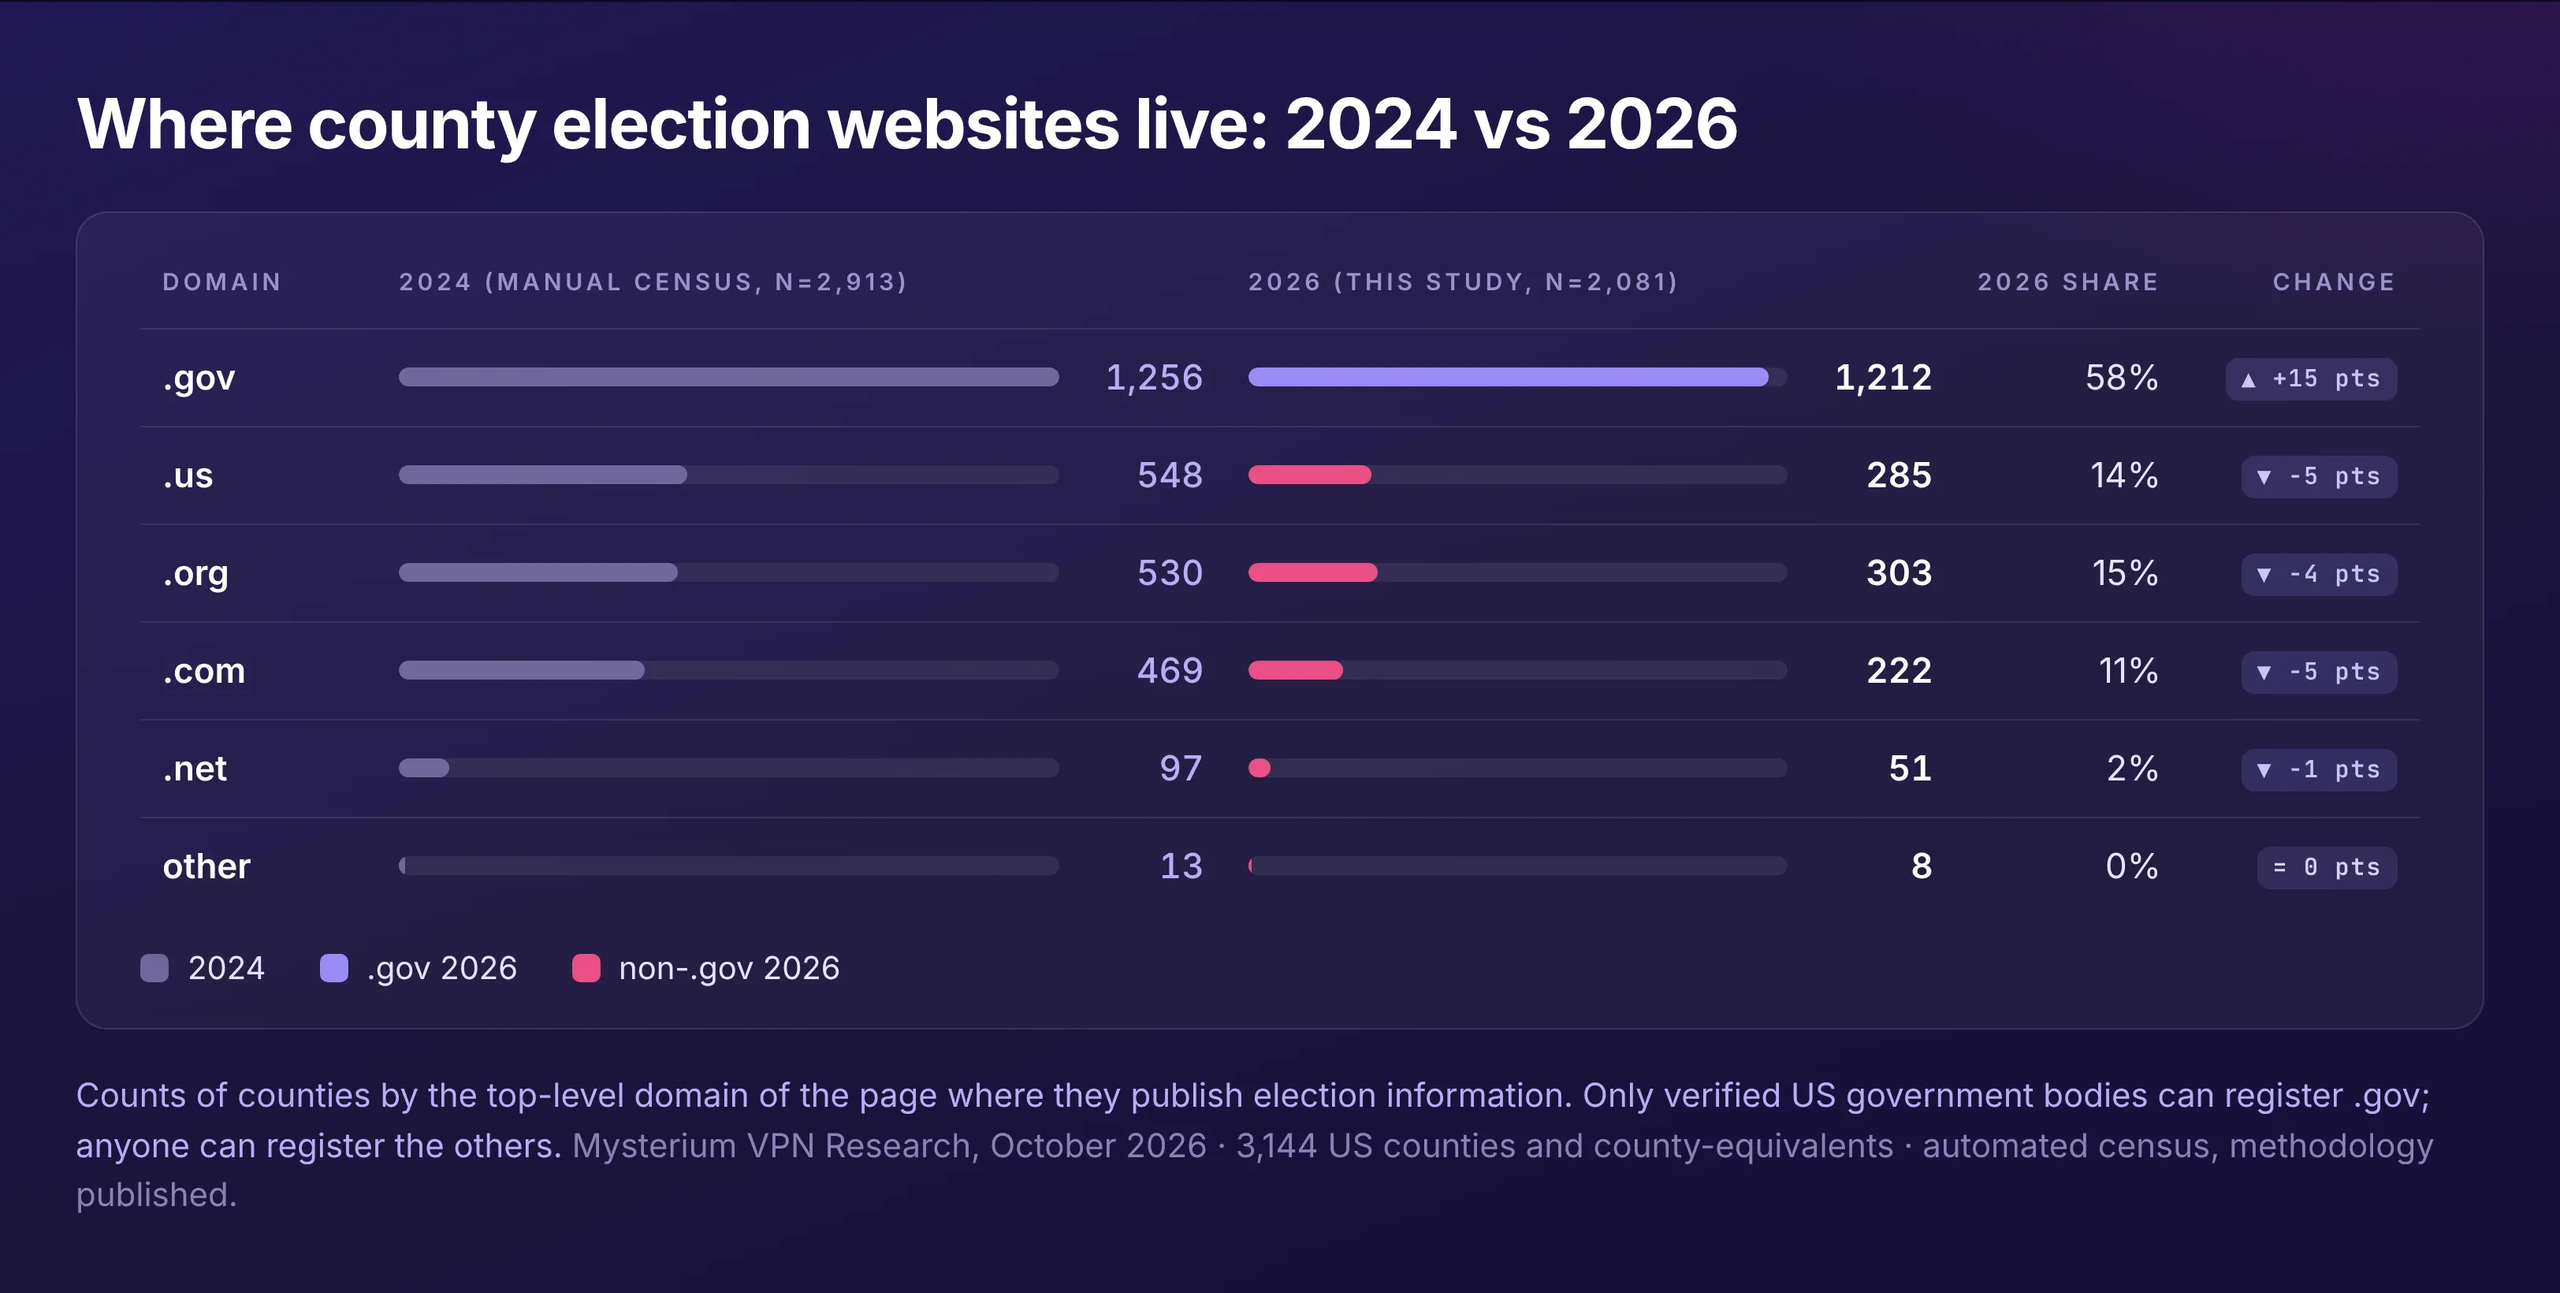
Election Website Security: 42% of US County Sites Still Lack .gov Domains
US election websites show improved security, but weak email protection, non-.gov domains and third-party tracking still expose voters to risks. Millions of Americans will use websites to check their registration, find polling places or track ballots before the November 3 election. However, a new study finds that many county election websites still have security weaknesses […]
 Security Affairs Breach
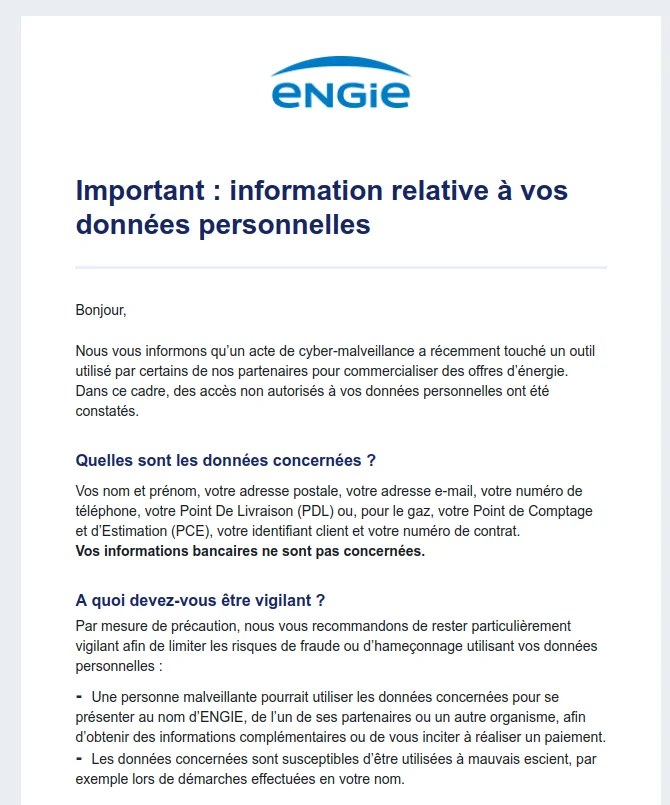
ENGIE Data Breach Exposes Customer Details and Energy Contracts
ENGIE says attackers accessed French customers’ contact and energy contract data through a partner sales tool. Banking data was not affected. French multinational energy company ENGIE warned customers in France that attackers accessed personal information through a sales tool used by some business partners. The exposed data includes contact details and energy contract information that […]
 Security Affairs Breach
Virtualine Domain Seized, but Allegedly Abusive Website Remains Online
The FBI seized Virtualine, a hosting service accused of supporting criminal sites, ignoring abuse reports and helping launder money from illegal activities The FBI seized the website of Virtualine, a hosting service that sold its services to criminals. The seized domain is virtualine.net, and the government says the site was used to commit and facilitate […]
 SecurityWeek Breach
HHS Filing Puts iRhythm Data Breach Toll at 8.2 Million
Hackers stole personal information and iRhythm account and device data from third-party-hosted business applications. The post HHS Filing Puts iRhythm Data Breach Toll at 8.2 Million appeared first on SecurityWeek.
 SecurityWeek Vuln
Chinese Hackers Quietly Used Low-Severity ESXi Logging Flaw as Zero-Day
CVE-2026-41709 allows attackers with administrative privileges to perform operations without being logged. The post Chinese Hackers Quietly Used Low-Severity ESXi Logging Flaw as Zero-Day appeared first on SecurityWeek.
Court strikes down West Virginia law barring disclosure of public officials’ personal data
A federal appellate court panel said West Virginia's version of Daniel's Law — meant to shield the personal data of police and other officials — is unconstitutional.
Japan Airlines warns of data breach as country grapples with multiple cyber incidents
Hackers stole passport numbers, frequent flyer numbers, email addresses and phone numbers for about 2,000 customers.
 Security Affairs Malware
Hive and Nefilim Ransomware Affiliate Gets 70 Months In Jail
Artem Stryzhak gets 70 months in prison for Hive and Nefilim ransomware attacks, while the FBI offers $11 million for his alleged co-conspirator. A federal court in Brooklyn has sentenced Artem Stryzhak, a Ukrainian national, to 70 months in prison for using ransomware to extort millions of dollars from victims. The U.S. Attorney’s Office for […]
European digital rights nonprofit noyb sues Scale AI for ‘invasive’ worker surveillance
Noyb alleges the platform in some cases records freelancers’ mouse clicks and keystrokes every few seconds and claims the collected information can be used to generate video documenting freelancers’ entire workday.
US sanctions Russians, North Koreans for laundering IT worker earnings
The U.S. Treasury Department sanctioned Russian and North Korean nationals for allegedly laundering the earnings of illicit IT workers on behalf of Pyongyang.
Moldova investigates possible foreign involvement in major government cyberattack
Prime Minister Vasile Tofan said the incident may be part of a broader campaign targeting both citizens' personal data and government digital infrastructure, according to local media reports.
UK to look at making software companies liable for cyber breaches
The new U.K. budget says the government will "consider where liability for cyber breaches should sit," potentially a landmark shift for a country that has relied on voluntary codes to encourage software vendors to improve security.
Belarusian hackers increasingly acting as proxies for Russia amid war in Ukraine
Belarus-linked hackers are increasingly aligning their cyber operations with Russia's interests in Ukraine, researchers said Wednesday.