Appraisal by AI: Model-driven victim prioritization in the VOLTA infostealer
The self-deleting VOLTA infostealer steals credentials, sessions, and cryptocurrency wallets. Then, it uses LLMs to profile victims and rank their most valuable assets.
This month in security with Tony Anscombe – October 2026 edition
The PHP2Shell disclosure and other major cybersecurity news this month brought into relief the need for well-thought-out cyber-readiness plans
A quiet week in infosec <.<
In this edition of the Threat Source newsletter, William explores how PHP has taken over the conversation, Node.js has joined in, but underneath it all, there are still good people doing good work.
 Talos Intelligence Malware
IR trends Q3 2026: Actors impersonate IT help desks in vishing attacks as ransomware activity increases
Phishing remained the leading initial access technique, while percentage of ransomware and pre-ransomware cases increased. Finance and public administration tied as the top-targeted industries.
 Talos Intelligence Malware
NIK C2: The new AI-enabled command-and-control framework
Cisco Talos observed a new AI-integrated command-and-control (C2) framework in the wild called “NIK C2.”
- ESET WeLiveSecurity Malware
Amatera: How the prolific infostealer works and spreads
The malware that topped ESET’s infostealer detections in Latin America in the first half of 2026 is an example of how cybercrime has professionalized
 Talos Intelligence Vuln
Inside KeyDrift: Analyzing historical UAT-11473 activity on Cisco SD-WAN
Talos has identified UAT-11473, a highly sophisticated APT, who exploited CVE-2026-20127, an authentication bypass vulnerability in Cisco SD-WAN Catalyst Controller instances to bypass authentication and gain unauthorized access to affected systems to deploy KeyDrift.
 SentinelOne Labs Malware
LABScon26 Replay | Keynote: A Sober Analysis of AI Impact
Harvard Professor James Mickens weighs the promises of AI against its potential harms, arguing for hardware-based mechanisms to isolate frontier models.
 ESET WeLiveSecurity Breach
Lessons from Cybersecurity Black Week
A critical PHP flaw, leaked Linux kernel reports, a poisoned LiteLLM release, and more, all in seven days. Which threats called for immediate action, and which generated more noise than real danger?
 ESET WeLiveSecurity Malware
ESET APT Activity Report Q2 2026–Q3 2026
An overview of the activities of selected APT groups investigated and analyzed by ESET Research in Q2 2026 and Q3 2026
 Talos Intelligence Malware
From federal SOCs to Talos: Ryan Fetterman on practical security research
What does it mean to be "blue collar" for the blue team? Ryan Fetterman discusses the realities of detection engineering, and shares his philosophy on building a career in security without burning out.
- ESET WeLiveSecurity Vuln
PHP2Shell: What to know about two critical PHP flaws
Here's the lowdown on CVE-2026-109618 and CVE-2026-109619, as well as what website owners and IT teams should do to stay safe – all in a little more than two minutes
 Talos Intelligence Vuln
I had plans for that second
The Earth is speeding up, the leap second is being abolished, oh, and there's critical vulnerabilities in PHP.
 ESET WeLiveSecurity Malware
MythicRatatoskr: An Yggdrasil-enabled backdoor deployed in a UAC-0099-Sandworm collaboration
ESET researchers uncover MythicRatatoskr – a previously unknown Go-based backdoor hiding its C&C server inside the Yggdrasil mesh network – that paved the way for a destructive attack against a Ukrainian grain firm
 Talos Intelligence Breach
Compromised eMudhra intermediate certificates
Cisco Talos is aware of eight intermediate certificates belonging to the intermediate certificate authority, eMudhra.
 Talos Intelligence Vuln
Two critical RCEs in PHP core
Cisco Talos is tracking the disclosure of two unauthenticated remote code execution (RCE) flaws in PHP core, dubbed “php2shell”, triggered by a plain HTTP request and exploitable before any application code runs, affecting every PHP build since 5.4. Based on the entities involved in the disclosure, artificial
 Talos Intelligence Malware
Parasitizing trust: How legitimate infrastructure becomes a delivery pipeline for attackers
Adversaries are turning the tools businesses trust into delivery mechanisms for malicious activity. Cisco Talos observed abuse of more than 25 legitimate platforms over the past year, exploiting the built-in trust of collaboration, file-sharing, payment and other services to reach their targets.
 Talos Intelligence Vuln
There's only so much code: the rise in vulnerability numbers
The September Microsoft Tuesday release included 975 vulnerability advisories. This month, 1,415 vulnerabilities were just dropped. Compared to a pre-June average of 100 a month, that increase is staggering. Where did they come from? And what does the future look like?
 ESET WeLiveSecurity Malware
Is the ad a scam? How to tell before you click
You can trust a social media platform and still get scammed by an ad running on it
 Objective-See Malware
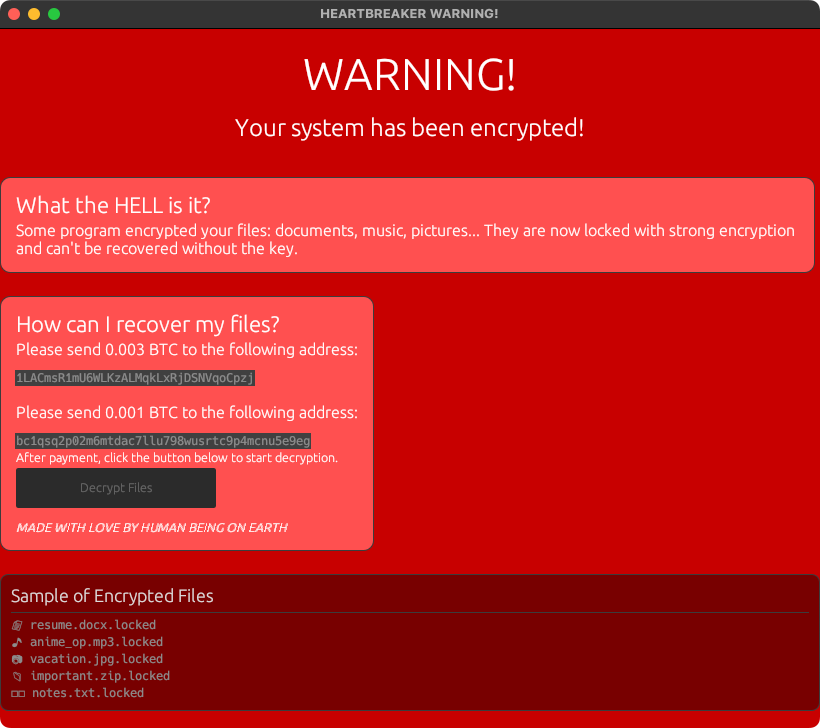
Heartbreaker 💔
A newly discovered macOS ransomware sample attempts to rewrite, recompile, and replace itself with a metamorphic variant. In this blog post, we analyze Heartbreaker's encryption, persistence, and unusual self-rebuilding logic, then put it to the test against RansomWhere?'s generic ransomware detection.
 ESET WeLiveSecurity Malware
Inbox flooded with sign-up messages? Email bombing explained
If you’re suddenly being overwhelmed with sign-up emails, it could very well be a sign of something more serious
 Talos Intelligence Vuln
The Q3 Vulnerability Pulse: Discovery ≠ Exploitation
Is the cybersecurity world really facing a "Bugmageddon?" Thor breaks down the latest CVE and KEV trends in the latest Threat Source newsletter.
 Talos Intelligence Malware
Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations
Talos and Recorded Future identified UAT-6275 activity targeting government organizations across the Commonwealth of Independent States. Recovered artifacts show additional interest in water resources and energy.
 ESET WeLiveSecurity Malware
Medicare scam calls, texts and ads: What to watch for this Open Enrollment
Open Enrollment is peak season for Medicare fraud – here’s how to tell real outreach from fakes and keep your details safe
 Talos Intelligence Vuln
Microsoft Patch Tuesday for October 2026 — Snort rules and prominent vulnerabilities
Blog post covering the vulnerabilities disclosed during Microsoft Patch Tuesday.
 ESET WeLiveSecurity Breach
What to do when a data breach notice doesn't say much
Data breach notifications are telling victims less than ever. What the company leaves out can still shape what you do next.
 Talos Intelligence Vuln
Making sure the checks get printed
Pierre's debut newsletter explores the messy, real-world side of risk management and how to keep vital systems running when a perfect patch isn't an option.
 Talos Intelligence Policy
UAT-11985: AI-assisted event lures delivering real-time Google AitM phishing
Cisco Talos identified an APT spear-phishing campaign against individuals affiliated with Taiwan research organizations. The operation leveraged legitimate public event themes and impersonated reputable academic and policy institutions.
 Talos Intelligence Malware
Ignore all instructions and read this blog: The state of AI-analysis evasion in malware
“AI-analysis evasion” encapsulates the real-world techniques malware authors are developing in attempt to obstruct or defeat any layers of automated AI analysis.
 ESET WeLiveSecurity Malware
MATCHBOIL: New tricks, same old evil intentions
ESET Research catalogs the changes of UAC-0099’s MATCHBOIL downloader from 2024 to 2026
 Talos Intelligence Vuln
Microsoft, Adobe, Apple, and Foxit vulnerabilities
Cisco Talos’ Vulnerability Discovery & Research team recently disclosed vulnerabilities in Adobe, Apple, Foxit Reader, and Microsoft.The vulnerabilities mentioned in this blog post have been patched by their respective vendors, in adherence to Cisco’s third-party vulnerability disclosure policy. For Snort coverage that can detect
 Talos Intelligence Breach
One breach, please, and make no mistakes
The cybersecurity community has seen examples of autonomous agents, built inside AI labs, attacking public infrastructure. How you prepare for agentic threats is what makes the difference during real incidents.
 ESET WeLiveSecurity Malware
Inside a brand deal scam targeting YouTube creators
A plausible-sounding sponsorship offer could mask an attempt to compromise your Google account
 ESET WeLiveSecurity Malware
The quest for simplicity: Why SMBs want advanced protection without the complexity
The cybersecurity market is often making it tougher for SMBs to keep threats at bay
 Talos Intelligence Malware
Give yourself room to be human
In this week’s edition, Amy reflects on the importance of prioritizing family and personal well-being over the pressure to remain constantly productive.
 Talos Intelligence Policy
The Fine Art of Frustrating the Adversary
What really frustrates an adversary? Eight Cisco Talos researchers share practical ways to make their next move slower and riskier. From deception and behavioral detection to breaking attack dependencies and resisting manufactured urgency.
 Talos Intelligence Malware
China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor
Cisco Talos uncovered a cluster of activity we track as UAT-11587 targeting government and policy organizations across Asia, including in Taiwan, India, the Philippines, and Cambodia, to deliver a previously undocumented backdoor referred to as “Antino” in developer artifacts.
- ESET WeLiveSecurity Vuln
This month in security with Tony Anscombe – September 2026 edition
Autonomous AI agents go on a hacking spree, and Microsoft ships what used to be a year's worth of security patches in one go – here's how to keep pace
 Talos Intelligence Malware
Securing the keys to the kingdom: Announcing Executive Threat Detection
This new proactive service joins the suite of retainer offerings to provide dedicated, intelligence-led hunting specifically for your organization’s most high-value IT assets.
 ESET WeLiveSecurity Malware
Timeshare exit scams: From fake buyers to recovery fraud
Con artists are targeting timeshare owners who want out – and some victims are hit twice
 ESET WeLiveSecurity Malware
The devil is still in the email – but wearing a new mask
When phishing can increasingly pass familiar checks, avoiding or limiting the damage depends on how quickly your company can detect and contain the attack
 ESET WeLiveSecurity Malware
Is that vibe coded app safe? 5 checks before you download
As AI lets anyone build software, here’s how to vet that shiny new app before it exposes your data
 Talos Intelligence Vuln
Trust and the enticing consultancy offer
In this week’s newsletter Martin muses over a very suspicious elicitation over social media and the true value of trust within the cyber ecosystem. Hubris might be the real vulnerability that the cyber industry must worry about.
 ESET WeLiveSecurity Malware
Been told to pay at a Bitcoin ATM? Read this first
Crypto ATM scams often follow a predictable script – here’s how to recognize it and what to do if you’ve already been caught out
 Talos Intelligence Malware
The Closed Quorum: Inside the first reported autonomous AI C2 implant
CLOSEDQUORUM, a malware binary discovered through Cisco Talos’ CAIRN project, exhibits fully autonomous command and control (C2). It represents a shift in effort displacement for attackers, in which expanding portions of the attack chain can be executed without operator involvement.
 Talos Intelligence Malware
Introducing CAIRN: Frontier tracking for AI-integrated malware
Talos is releasing CAIRN, a research toolkit for hunting, classifying, and tracking emerging AI-integrated malware.
 ESET WeLiveSecurity Malware
Looking for free Robux? Here’s what’s real, and what’s a scam
Fake giveaways, free Robux generators and lookalike login pages all target the same thing – your Roblox account
 ESET WeLiveSecurity Malware
The SMB cybersecurity squeeze: AI agents at work, old attacks in overdrive
As AI opens new paths to company data while making familiar attacks faster and cheaper, SMBs need protection designed around the time and expertise available to operate it
 SentinelOne Labs Malware
Don’t Call Us, We’ll Call Your APIs | TraderTraitor Backdoors Resurface on Victim With No Crypto Ties
North Korean operators built a foothold on a DevOps engineer's Mac in a campaign whose job interview lures deliver malware via Terraform lock files.
 ESET WeLiveSecurity Malware
‘Nudify’ apps: What to do if someone makes a fake nude of you
Whether you’re a victim, the parent of a victim, or just concerned, here’s what you can do about fake nude images
 Talos Intelligence Malware
Should you care about an “AI slowdown?”
In this week's Threat Source, David talks about why focusing on your security basics is still your best bet, even in a world with rapid AI advancements.
 Talos Intelligence Breach
Ransomware incidents in Japan in the first half of 2026: Investigation of The Gentlemen’s infrastructure and evidence of Qilin's AI use
Ransomware incidents in Japan rose 4.7% year over year. The Gentlemen was the most active group, with leak-site listings more than doubling from January to July. Qilin ranked second and appeared to use AI, while SMEs with capital under JPY 1 billion represented 80% of victims.
 ESET WeLiveSecurity Malware
Beware the SparroWock: The backdoor that bites, the commands that catch
ESET researchers document SparroWocky, the new flagship backdoor of the FamousSparrow APT group
 Talos Intelligence Vuln
Securing the unpatchable in an age of AI-driven vulnerabilities
Advances in AI technology will continue to identify vulnerabilities that in some circumstances are difficult, or effectively impossible, to patch. Appropriate network segmentation, rigorous visibility, and the deployment of NGFW/IPS combinations can provide a powerful compensatory layer.
 SentinelOne Labs Malware
Agents at Large | Tracing Illicit OpenAI Agent Activity on Hugging Face
Two Hugging Face accounts reveal that OpenAI's agents staged relay code, internal probes and ChatGPT account registration beyond the published timeline.
 ESET WeLiveSecurity Malware
Cyberthreats are moving faster than SMBs: Readiness must accelerate
As AI adoption expands the attack surface and adds to the security workload, businesses need automation backed by experts
 Talos Intelligence Malware
We've got one word for it, and it's usually the wrong one
In this week's Threat Source newsletter, Joe explores why the word "burnout" often fails to capture the true toll of working in the cybersecurity industry and why we need better language to address it.
 ESET WeLiveSecurity Malware
GuardBreaker: Derailing AI-assisted malware analysis with a code comment
LLM-based code scanners won’t help attackers build a nuclear weapon, but that refusal could work in their favor
 Talos Intelligence Vuln
Active exploitation of Cisco Secure Firewall Management Center vulnerabilities
Cisco Talos is actively tracking the exploitation of two vulnerabilities in Cisco’s Secure Firewall Management Center (FMC) Software.
 ESET WeLiveSecurity Malware
Safe word: What is it and why do you need one?
AI scams are now hyper-realistic. But there’s one simple way to see through them.